OpenCode: reported theft of Anthropic, OpenAI and Google API keys
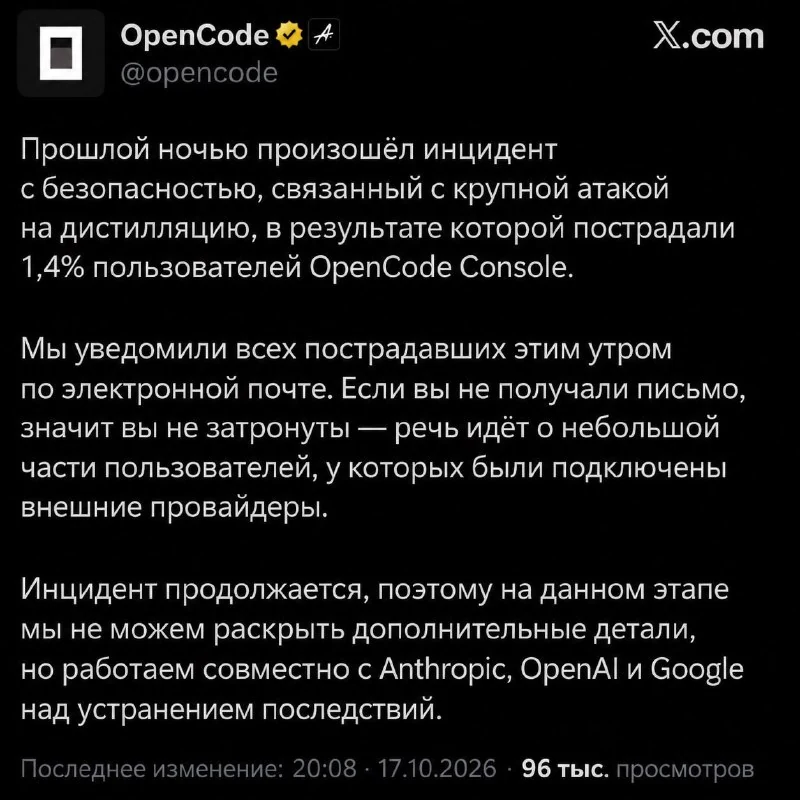
OpenCode developers said a security incident affected 1.4% of users; API keys for Anthropic, OpenAI, Google and other AI services should be replaced.
What happened
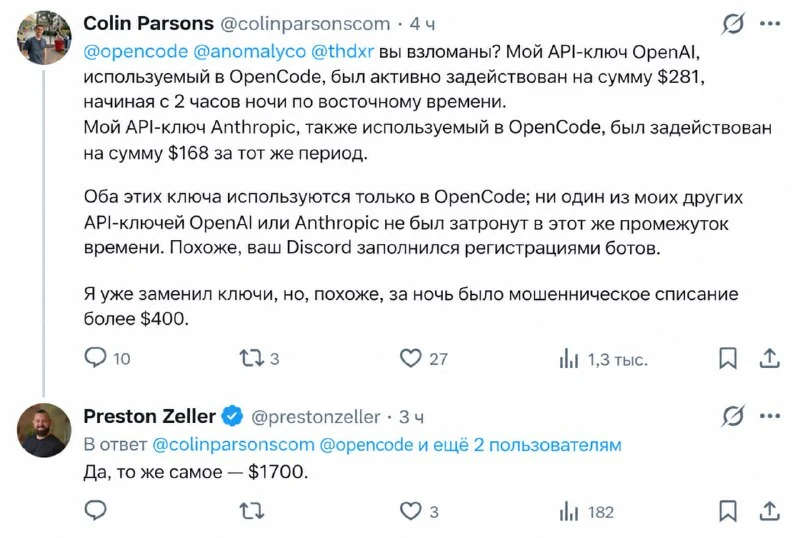
OpenCode developers reported a security incident in which attackers allegedly harvested users' API keys. Services mentioned include Anthropic, OpenAI, Google and other AI platforms.
According to the developers, only 1.4% of users were affected.
What to do
- revoke and rotate any API keys used with OpenCode;
- review activity in Anthropic, OpenAI, Google and other provider dashboards;
- check request logs and billing;
- enable additional account protections where available.
Why it matters
API keys grant direct access to paid and sensitive AI services. Their compromise can lead to unauthorized usage, unexpected bills and data exposure, so key rotation is the minimum necessary response.
Why it matters
AnalysisStolen API keys can turn an AI coding tool into a channel for unauthorized spending and data leakage, making immediate key rotation essential.
Discuss in community
Share your questions and insights with developers