Microsoft Introduces Execution Containers for AI Agents
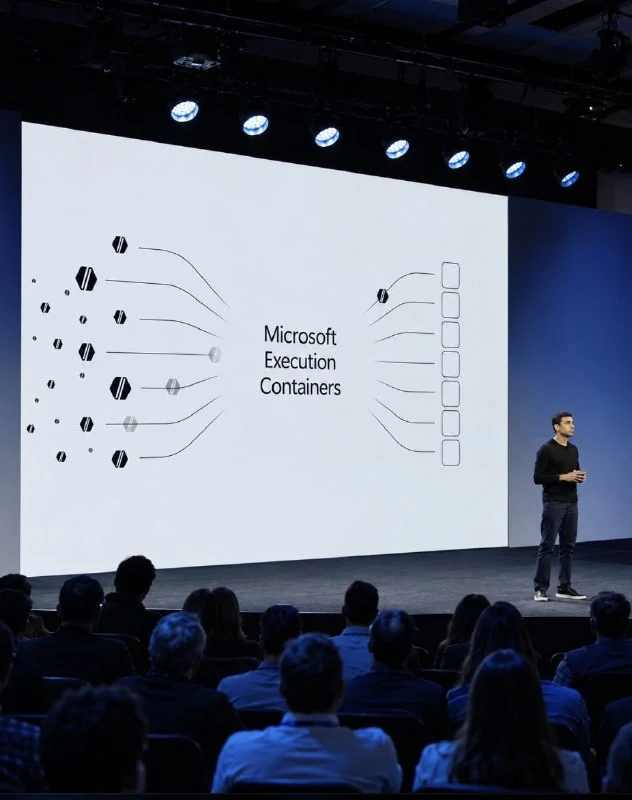
Microsoft Execution Containers (MXC) gives developers policy-based control over AI agent access to files, networks, and system resources on Windows, Linux, and macOS.
Microsoft has introduced a new containerization system for AI agents that works on Windows, Linux, and macOS.
It is called Microsoft Execution Containers (MXC) and lets developers precisely control which files, networks, and system resources an agent can access.
For example, an agent can edit project files and run required tools, but it cannot reach the user's personal files or modify configurations that are allowed only for reading.
The key difference is that the restrictions operate independently of the agent itself: the agent cannot grant itself additional permissions.
MXC uses isolation environments specific to each operating system, including Bubblewrap on Linux. Management is handled through a unified JSON configuration and SDK.
GitHub Copilot, OpenAI Codex, Replit, and OpenClaw already support the system. Claude Code support is planned.
Why it matters
AnalysisIt shifts AI agent safety from prompt-level guardrails to enforceable OS boundaries, reducing the risk of accidental or malicious privilege escalation.
Discuss in community
Share your questions and insights with developers