Google paid $250,000 to a startup that found a Chrome vulnerability with GPT-5.6 Sol
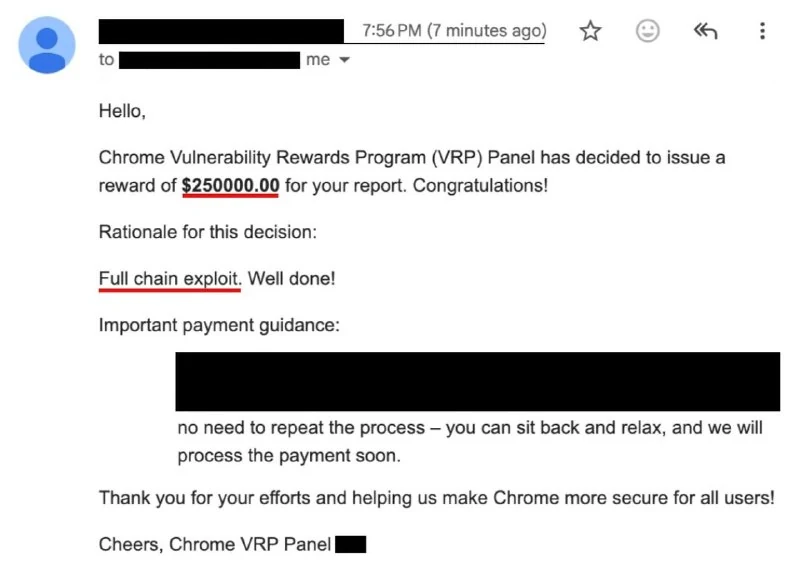
XBOW and GPT-5.6 Sol built a full-chain Chrome exploit in six days and earned a $250,000 bug bounty from Google.
Chrome is considered one of the most secure software products in the world, and this is only the second time Google has paid such a large bug bounty.
XBOW is a startup building an autonomous AI system that finds and exploits vulnerabilities on its own. In January, the team set a goal: create a full-chain exploit for Chrome by Black Hat in August.
They worked on it for six months, but when they submitted the chain to Google, the company said it already knew about one of the bugs used. By then, the team was already in Las Vegas for Black Hat, so they decided to try to find another exploit under extreme time pressure.
They succeeded. Four people plus GPT-5.6 Sol assembled the chain in just six days. Google later paid them $250,000 for it, while their token costs were around $40,000.
XBOW CEO Oege de Moor said that such work used to take his team months. In his view, the turning point in vulnerability discovery with agents has already been passed, and the cost of this kind of research has collapsed for both attackers and defenders. Defenders’ only advantage is that they can check their own code first.
Why it matters
AnalysisThe case shows that AI agents can now compress complex vulnerability research in highly protected products from months to days, changing the economics of offensive and defensive security.
Discuss in community
Share your questions and insights with developers