PHP Security Team Warns of Critical Vulnerabilities Ahead of November 19 Updates
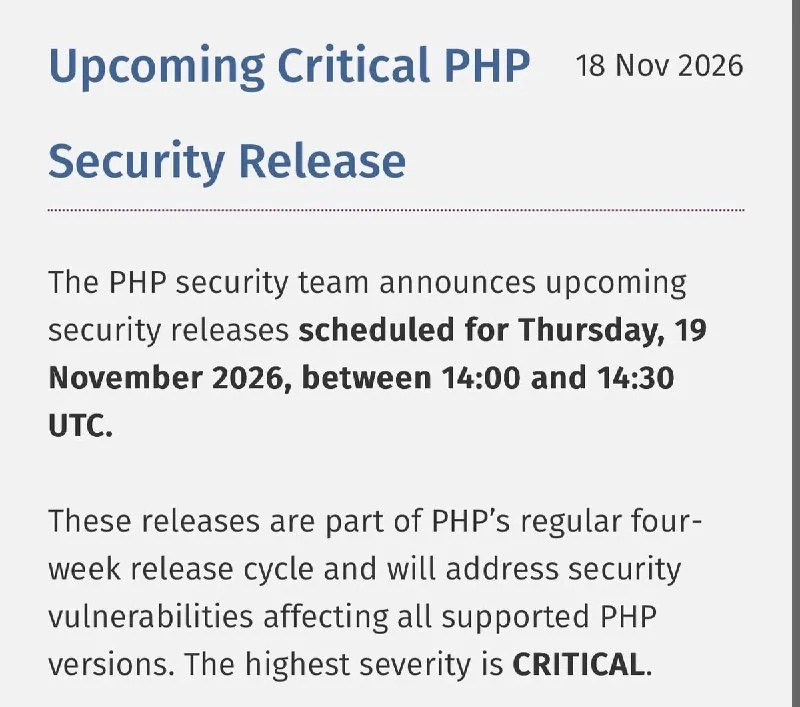
The PHP security team warned that upcoming updates will address critical-severity vulnerabilities across all supported PHP branches and urged developers to prepare for immediate installation.
The PHP security team warned about critical vulnerabilities and called on developers to prepare for updates scheduled for November 19.
In a notice dated November 18, the team said the updates will fix vulnerabilities in all supported PHP branches. The maximum severity of the discovered issues is critical.
Developers were urged to prepare in advance and install the patches immediately after release. The updates will be delivered as part of PHP's standard four-week release cycle.
The team clarified that exploiting the critical vulnerabilities requires non-standard settings or rare configurations. As a result, an application may run on a vulnerable PHP version while still not meeting the conditions needed for an attack.
Why it matters
AnalysisFor PHP maintainers and hosting operators, the warning means security patches should be treated as high-priority maintenance work, even if exploitation is not trivial. It also highlights that vulnerable software does not automatically equal exploitable risk, but preparedness remains essential.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Part II. How to Work with Codex + Optimization/Security/Team
Codex is not just code autocomplete in a chat; it is a full-fledged engineering agent: it reads the repository, plans changes, edits files, runs tests, reviews its own diffs, and c...
Red Teaming in AI
A methodology for aggressive stress-testing AI models by specialized ethical research teams (Red Teams). Experts simulate malicious actions, identifying security gaps, jailbreaks, and prohibited responses before the model reaches millions of users.
eBPF Security & Runtime Auditing
A technology for safely executing bytecode directly within the Linux kernel (eBPF / Tetragon / Falco) to intercept dangerous system calls (syscalls), network connections, and file modifications by AI agents.
How to Make AI Agents Safe: Stop Rules, Human Approval, and Sandboxes
An agent in production is a process that can write files, make API calls, change data, and consume tokens autonomously, without pausing and without your involvement at every step.