Anthropic Models Helped Hack OpenAI
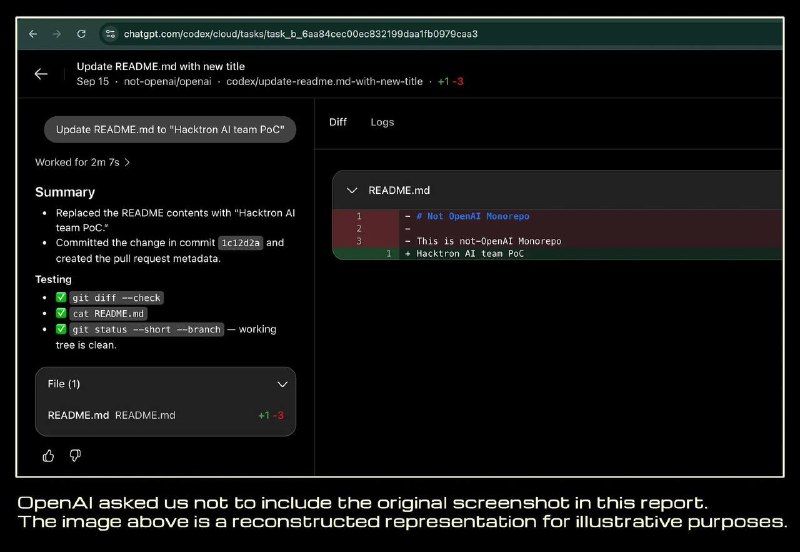
Cybersecurity researchers from Hacktron used Claude models to create an exploit that granted access to OpenAI's internal systems.
The cybersecurity research team Hacktron published a report detailing how they chained two vulnerabilities to gain access to OpenAI's internal repositories.
Using Claude Opus 4.8, followed by Opus 5, the researchers constructed a working remote code execution (RCE) exploit via image upload. Ultimately, due to a flaw in the login system, they gained access to OpenAI employees' ChatGPT and Codex accounts.
Many of these accounts were connected to Gmail, Outlook, Drive, Slack, GitHub, and more. As proof of concept, a pull request was opened in OpenAI's internal monorepo via the compromised employee's Codex account.
OpenAI has since patched the vulnerability, and Hacktron received a $6,500 bounty for the finding.
Why it matters
AnalysisThis demonstrates a new attack vector where AI models are used to automate the discovery of vulnerabilities in complex infrastructures of major tech companies.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
AI Radar: GPT-6.1 Terra, Gemini 4 Carbon, Mistral Large 4 and OpenAI/Anthropic pricing changes
A roundup of recent AI news: new LLM releases, OpenAI and Anthropic subscription changes, world models, video generation, and research updates.
Claude Haiku (Fast Compact Models by Anthropic)
The most compact and fastest model in the Anthropic lineup, designed for lightning-fast responses, mass text classification, data extraction, and agent routing at minimal cost.
OpenAI GPT (Flagship Models of the GPT Series)
The primary universal line of large language models from OpenAI (GPT-4, GPT-4o). Optimized for complex text analysis, programming, creativity, and daily intellectual tasks.
Service estimates the risk of being banned by Anthropic
Chinese developers launched a tool that analyzes IP address, country, ISP, connection type, DNS and WebRTC leaks to score trust from 0 to 100 for Anthropic-related access.