OpenAI Releases CLI and TypeScript SDK for Code Vulnerability Scanning
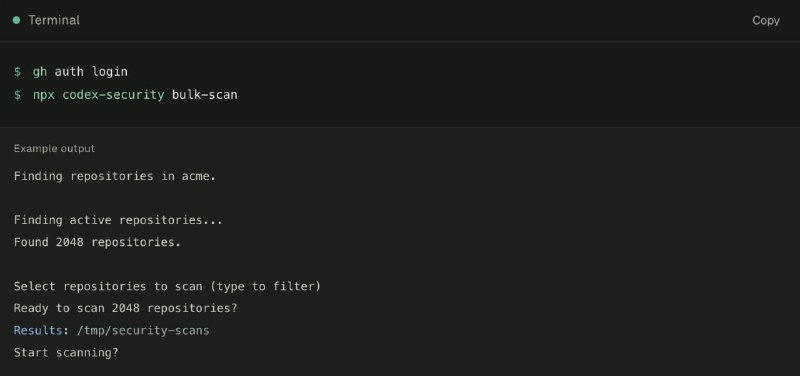
OpenAI has introduced a new CLI and TypeScript SDK for detecting vulnerabilities in code. The tool allows developers to scan repositories and integrate security checks into CI/CD.
OpenAI Releases CLI and TypeScript SDK for Code Vulnerability Scanning
OpenAI has quietly rolled out a new tool that enables developers to scan their repositories for code vulnerabilities. This tool, available as a CLI and TypeScript SDK, was noticed on Hacker News before the company officially announced it.
Key Features:
- Scanning repositories for vulnerabilities.
- Saving and tracking identified issues between runs.
- Checking if vulnerabilities have been fixed.
- Integrating security checks directly into CI/CD.
This is still an early version of the tool, and OpenAI is actively gathering feedback for further improvements.
Why it matters
AnalysisThis tool is crucial for developers as it automates the process of detecting vulnerabilities in code, enhancing software security.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Part II. How to Work with Codex + Optimization/Security/Team
Codex is not just code autocomplete in a chat; it is a full-fledged engineering agent: it reads the repository, plans changes, edits files, runs tests, reviews its own diffs, and c...
Codex Skills for Beginners: Automating AI Agent Workflows
A comprehensive hands-on guide to building and executing Codex Skills: SKILL.md anatomy, explicit vs. auto-triggering, skills vs. scripts vs. tools, Skills API, and safety boundaries.
OpenAI GPT (Flagship Models of the GPT Series)
The primary universal line of large language models from OpenAI (GPT-4, GPT-4o). Optimized for complex text analysis, programming, creativity, and daily intellectual tasks.
Hallucinated Dependencies in Code
A dangerous variant of neural network hallucinations in programming. The model fabricates plausible yet non-existent libraries and npm/PyPI packages, creating critical security vulnerabilities (Slopsquatting).