New PS5 Jailbreak: Relapse Exploit for Firmware 7.00–13.60
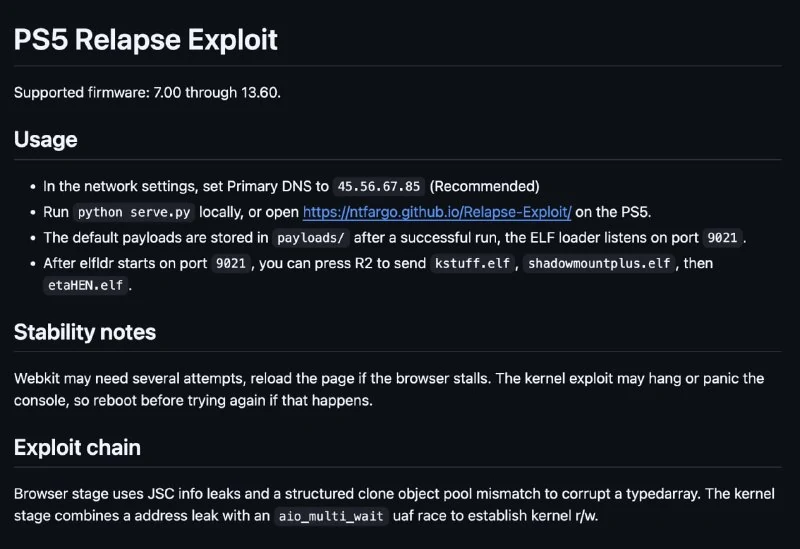
A new exploit named Relapse has been released, enabling PS5 jailbreaks on firmware versions 7.00 through 13.60 via WebKit and kernel vulnerabilities.
Developers have released a new tool called Relapse-Exploit, which enables jailbreaking PlayStation 5 consoles on all firmware versions from 7.00 to 13.60. Early testers report that the process takes only seconds and works even on the PS5 Pro model.
How It Works
To launch the exploit, users simply need to open a specific website in the console's built-in browser. No external hardware or complex file system manipulations are required.
Technical Details
The exploit relies on a chain of vulnerabilities:
- WebKit Vulnerability: A bug in the browser engine is used to gain initial access.
- Kernel Use-After-Free: The exploit then leverages a use-after-free race condition in the operating system kernel.
This combination grants full read and write access to kernel memory, which is a critical step for loading payloads. This opens the door for installing homebrew applications and creating game backups.
Why it matters
AnalysisThis is a significant development for the enthusiast and security research community, as it expands modification capabilities for PS5 on current firmware versions, including the PS5 Pro, without requiring complex hardware methods.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Indirect Prompt Injection Defense
A comprehensive set of architectural and software methods to protect autonomous AI agents from hidden instructions placed by attackers in external web pages, documents, or APIs.
Red Teaming in AI
A methodology for aggressive stress-testing AI models by specialized ethical research teams (Red Teams). Experts simulate malicious actions, identifying security gaps, jailbreaks, and prohibited responses before the model reaches millions of users.
Part II. How to Work with Codex + Optimization/Security/Team
Codex is not just code autocomplete in a chat; it is a full-fledged engineering agent: it reads the repository, plans changes, edits files, runs tests, reviews its own diffs, and c...
How to Make AI Agents Safe: Stop Rules, Human Approval, and Sandboxes
An agent in production is a process that can write files, make API calls, change data, and consume tokens autonomously, without pausing and without your involvement at every step.