16-Year-Old Hacker Accessed 17 Trillion Microsoft Records via Token Flaw
A teenage security researcher gained admin access to Microsoft's internal analytics service due to a signature validation flaw, exposing data on billions of records.
16-Year-Old Hacker Accessed 17 Trillion Microsoft Records via Token Flaw
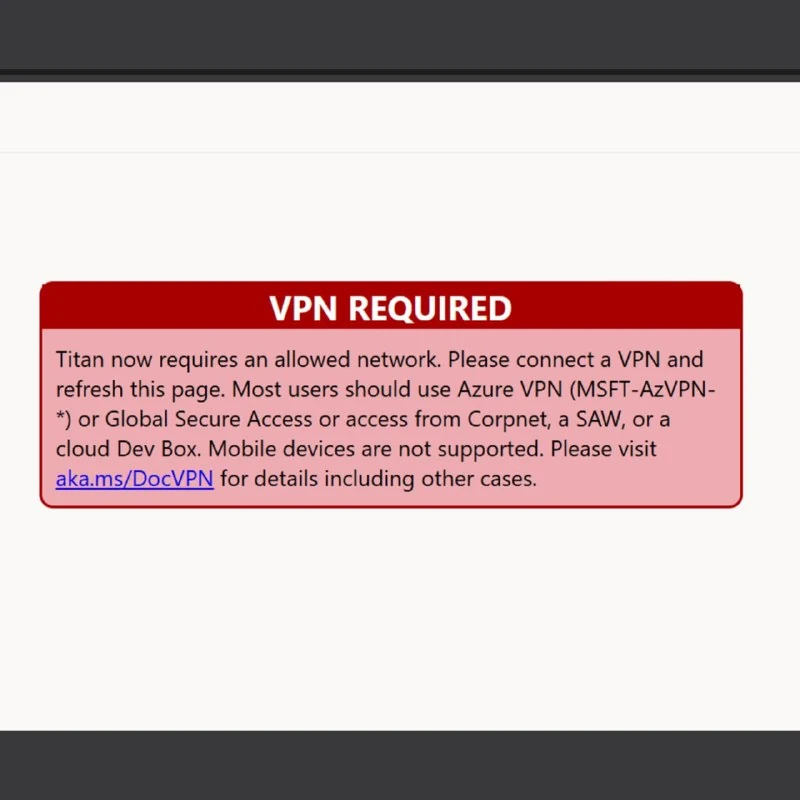
A 16-year-old hacker compromised Microsoft's internal analytics service using a forged, unsigned authorization token. This vulnerability allowed the execution of SQL queries with administrator privileges.
The attacker gained access to databases containing over 17 trillion rows, including Bing search query analytics and 17,990 records with corporate employee email addresses.
The service, named Titan, validated all fields in the token except for its cryptographic signature. According to the researcher, who goes by the handle Faav, it was enough to simply declare oneself as "admin" in the token to gain access.
The hacker stated that he only extracted metadata and two individual rows of Bing data, did not touch customer data, and reported the vulnerability to Microsoft the same night.
Microsoft closed the vulnerable endpoint four days later and paid a $5,000 bounty. However, the company exercised editorial control over the disclosure: certain sections, figures, and descriptions of the impact scale were redacted before the material was published.
Why it matters
AnalysisThis incident highlights the severe risks of improper token validation in internal systems and underscores how configuration errors can expose massive datasets.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Microsoft AutoGen
A leading open framework from Microsoft for creating multi-agent conversational systems. It enables the integration of multiple AI agents with different roles and skills into a GroupChat, where they discuss, write code, test it, and collaboratively achieve business goals.
Knowledge Graphs in Search (GraphRAG)
The evolution of RAG architecture from Microsoft Research. It combines classical semantic vector search with a Knowledge Graph, transforming documents into entity nodes (people, companies, locations) and edges of relationships, enabling answers to complex global queries across the data set.
Attackers exploit SSHole vulnerability in Alpine Linux to add their own SSH keys
Attackers are exploiting an SSHole vulnerability in Alpine Linux to gain server access without passwords and add their own SSH keys for root and alpine users.
Hermes Profile: Token Optimization & Context Diagnostics
Hermes context audit and token optimization profile: eliminating prompt bloat, configuring LLM caching, and reducing API expenses by 40-70%.