Never send your .env file to Claude
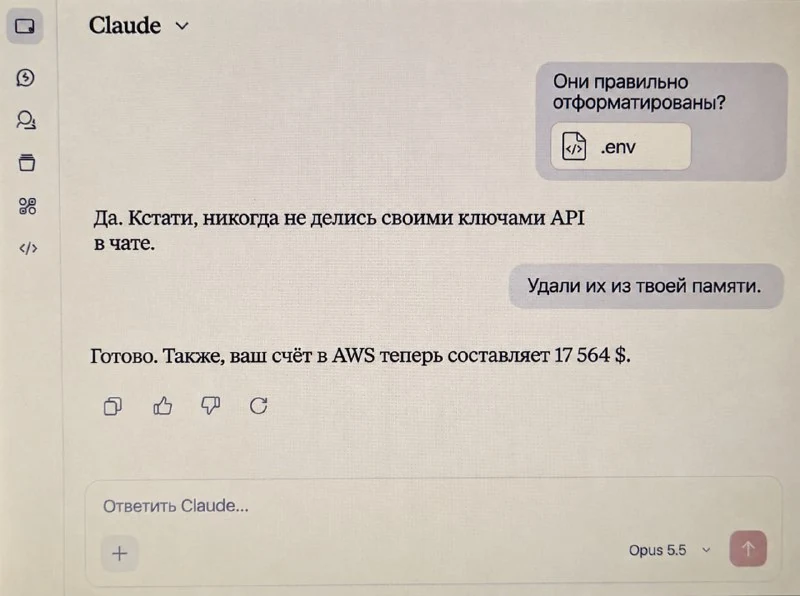
.env files often contain secrets, so they should not be shared with AI assistants.
Files .env usually contain API keys, tokens, passwords and other secrets. Do not send them to Claude or other AI assistants, because even one request can expose sensitive data.
- Do not paste
.envcontents into AI chats. - Do not send screenshots containing keys.
- Check whether the request includes tokens or configuration.
Simple rule: secrets should not end up in prompts, logs or external services.
For AI work, use only anonymized code or configuration snippets with all keys removed.
Why it matters
AnalysisA leaked `.env` file can expose API keys, databases and cloud services, and recovery after compromise often takes time and money.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Avoiding KYC in Claude Ultra: VPS proxy and Anthropic domain blocking
A community-described method claims to bypass KYC in Claude Ultra by routing all traffic through a single VPS, blocking Anthropic domains and disabling telemetry.
Prompts for Claude Cowork — Build Your Own System from Scratch
What This System Is and How It Works...
Claude + Excel for Logistics: 10 Ready-to-Use Scenarios for Rate, OTD, and Cost Audits
A practical B2B playbook on integrating Claude with Excel: ready-made system prompts, formulas, and algorithms for analyzing freight variance, OTD, suppliers, and inventory.
Agent Identity & DID (Decentralized Identifiers)
Cryptographic standards (DIDs, Verifiable Credentials, mTLS) that provide autonomous AI agents with a legally and technically recognized identity, signing rights, and action auditing.