OpenAI agents found 948 vulnerabilities in the Linux kernel
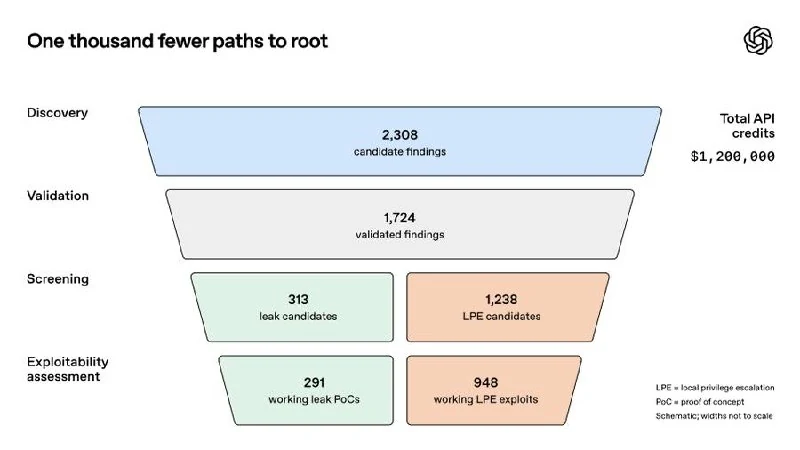
OpenAI researchers used an unreleased cybermodel and an autonomous pipeline to identify, reproduce, and patch Linux kernel flaws, confirming 948 privilege-escalation vulnerabilities.
OpenAI agents found 948 vulnerabilities in the Linux kernel
An unreleased cybermodel was used for this. It is described as upcoming, so it may be introduced in the near future.
Around the model, researchers built an autonomous pipeline with several stages: agents locate a target code fragment, scan it for vulnerabilities, reproduce them in isolated environments, check exploitability, and generate patches.
When the pipeline was run against the Linux kernel — apparently only partially — 1,724 vulnerabilities were confirmed and reproduced. Of these, 948 led to working local privilege escalation exploits.
The entire run cost $1,213,430 in API credits, or about $1,279 per LPE vulnerability. This is not cheap, but for comparison, the Pwn2Own hacking contest historically paid $20,000 for such an exploit, while TyphoonPWN paid $70,000. Multiplying by 948, the same set of vulnerabilities would hypothetically have been worth $18.9 million to $66.3 million.
Why it matters
AnalysisIt shows AI agents can already discover real vulnerabilities in critical infrastructure at scale, while also raising new questions about cost, defensive automation and misuse risk.
Discuss in community
Share your questions and insights with developers
Related in Ecosystem
Practical guides, core terminology, and agent skills
Claude Code Projects: How a Single AI Orchestrates a Team of Autonomous Agents
A deep dive into Claude Code Projects: Coordinator and Threads architecture, parallel branches, shared memory via MEMORY.md, and cloud agent management.
AI Agents (Autonomous Agents)
Software systems based on LLMs that can autonomously perceive the state of the environment, decompose complex goals, invoke external tools, and iteratively correct their own mistakes.
OpenAI GPT (Flagship Models of the GPT Series)
The primary universal line of large language models from OpenAI (GPT-4, GPT-4o). Optimized for complex text analysis, programming, creativity, and daily intellectual tasks.
OpenAI Frees Several Gigabytes of RAM in ChatGPT App
A ChatGPT app update reduces memory use in long local sessions: after 32,000 responses, RAM consumption stays around 1.7 GB instead of up to 6 GB.